






























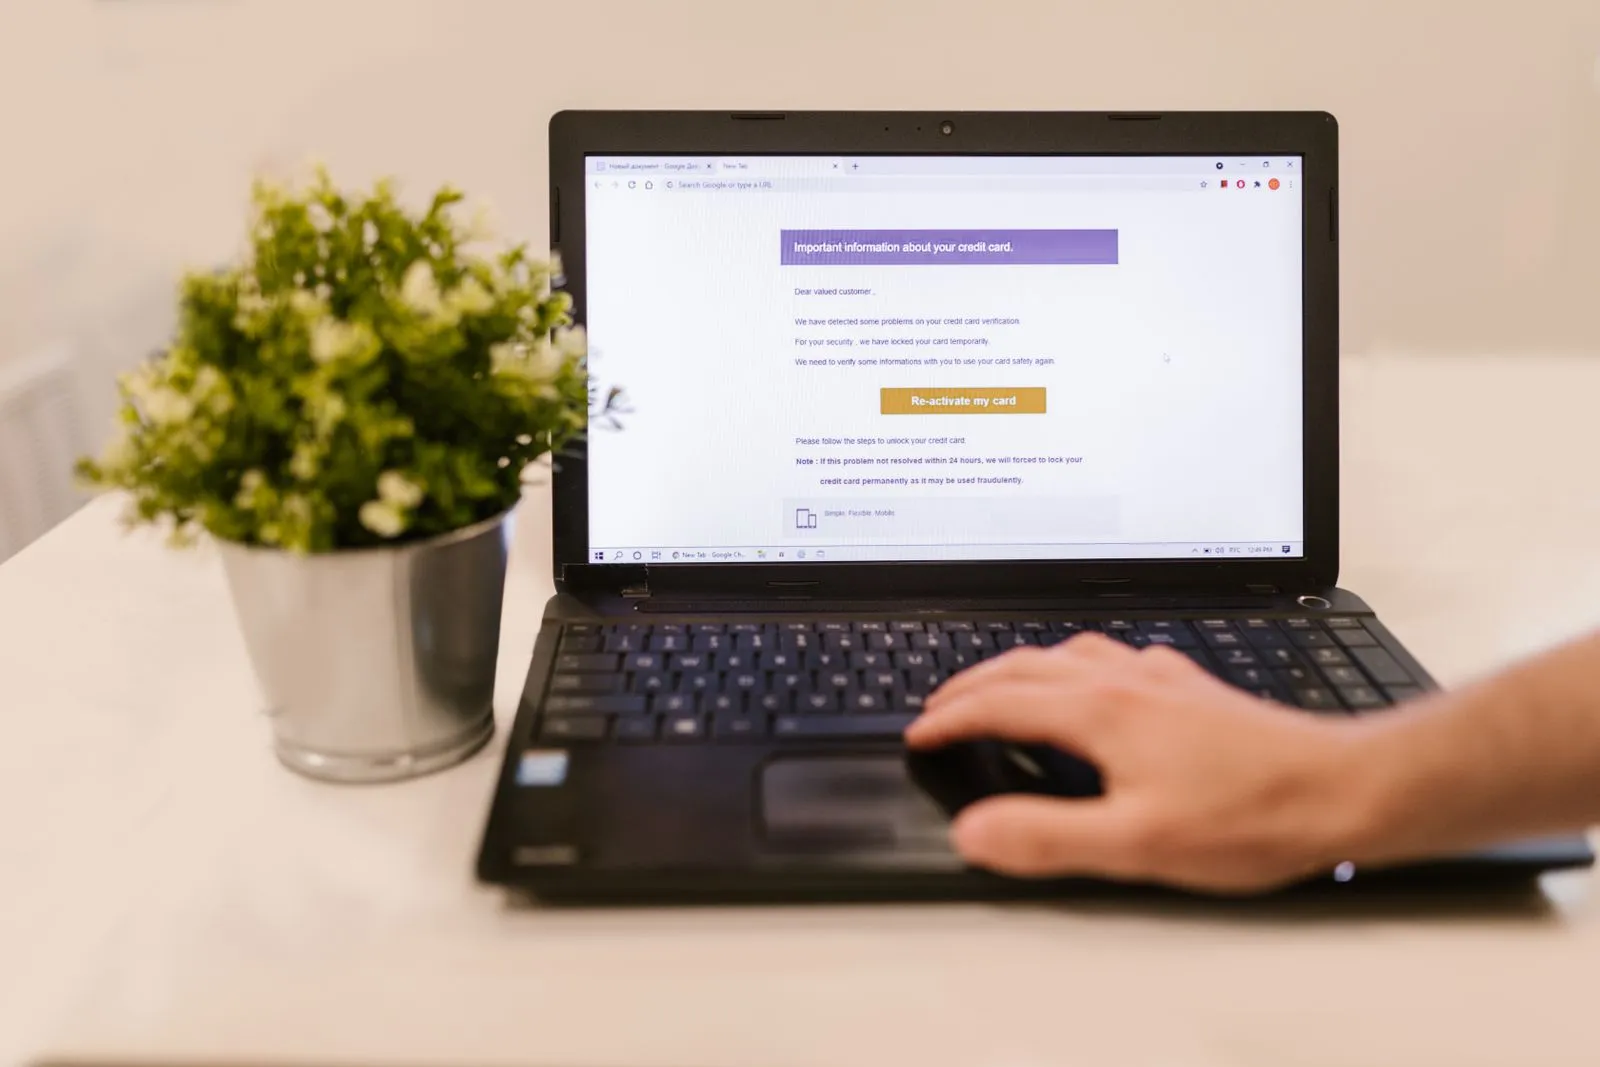
01
Phishing and social engineering
The team recognizes the risk and knows who to pass the incident on to.
Cyber Security · Course
First hour incident decides. We will teach management and operations phishing, protect accounts and data and follow a clear plan.
Division Director GBH Cyber
Your cybersecurity is not driven by a marketer, but by an engineer.
As a senior software engineer, he worked at IBM and at Trezor (SatoshiLabs), where he participated in the development of the Trezor Suite. At GBH, he connects cyber security with the group's physical infrastructure.
1 day
practical team course
10–25
people from management, IT and operations
NIS2
comprehensible for management
First hour
what to do in an incident
Practical impact
People need to know who to call, what to disconnect and what to let run.
Sunday course cyber security into separate layers. Accounts, dates, the physical operation and the roles of people will be linked into one procedure so that no one improvises during an incident.
Accounts, backups and critical data. Do you know who manages them and how to restore them?
The network, cameras and building mode run continuously. In the course, we connect them with data into one procedure.
Management, IT and reception. Everyone knows what to do in the first hour of an incident.
The course is for people who incident they pick up the phone, open the door or make traffic decisions.
01
The team recognizes the risk and knows who to pass the incident on to.
02
Accounts, cameras and administration have an owner.
03
Critical data can be restored on a schedule.
04
Cyber security also includes the building, cameras and entrances.
05
First phone call, decision and isolation.
06
We will translate duties into steps for leadership.
We do not deal with cyber security in isolation. We connect it with people, building and management decision-making.
We go through accounts, data, cameras, suppliers and crisis contacts.
Phishing, lost device, data leak, camera outage.
Management, IT, reception, operation and communication in one procedure.
What to change now, what to plan and what belongs to the audit.
01
You protect student data, teacher accounts and cameras. In the course, you will receive a clear procedure, not another directive in a drawer.
02
When a cyberattack stops production or billing, you decide. You will learn what to do in the first hour and who to call.
03
You manage the network, accounts and backups yourself. You'll take away a procedure that you can handle even without a Security Oversight Center (SOC).
04
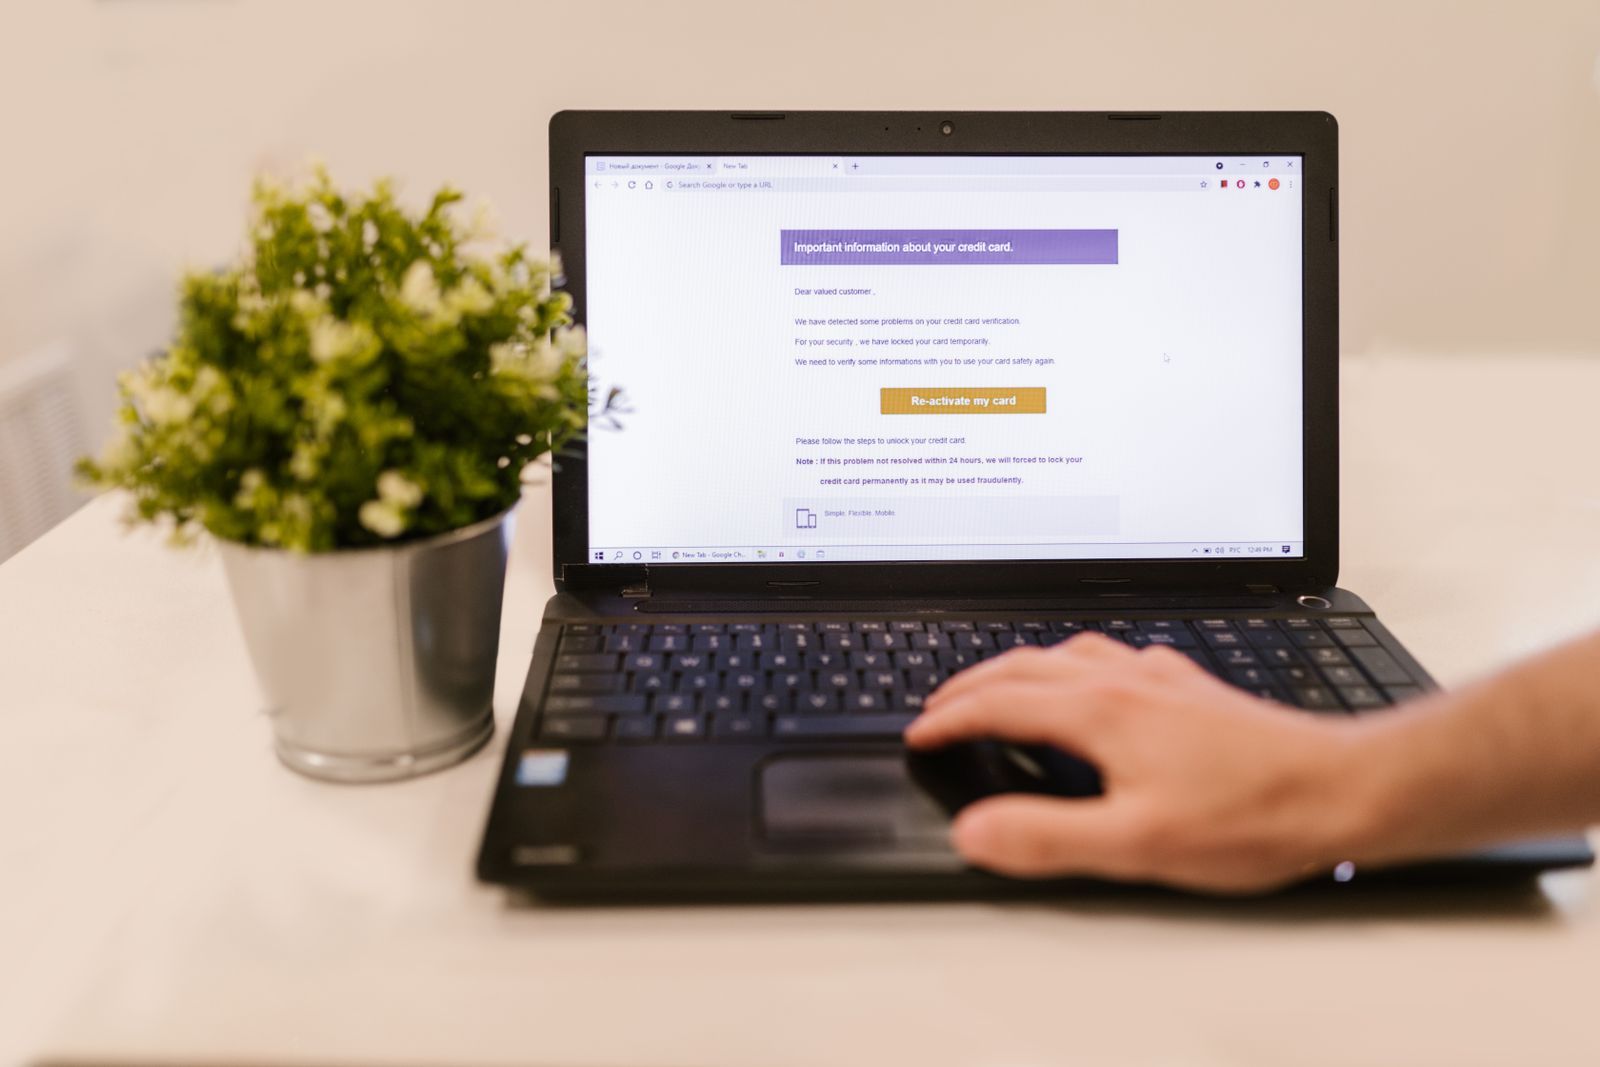
An attack can start with one click on the reception desk. You'll learn to recognize phishing before you open an attachment and know who to report it to.
05
We will translate the obligations according to NIS2 into steps that you can defend in front of management and the regulator.
06
Instead of improvising, you leave with a plan: who isolates compromised devices, who communicates, and who makes operational decisions.

The course connects employees, account managers, reception and management. We rehearse the first hour: how to recognize an attack, who to pass it on to, what to limit and how to maintain traffic.
Know the attack
Submit an incident
Restrict access
Keep running
The first hour of the incident
Who's calling What to turn off. To whom to pass.
A technical problem quickly becomes an operational crisis. The course will give people a concrete procedure.
Publicly documented incidents from the Czech Republic that were triggered by one click or an open attachment. The course rehearses this very moment: how phishing know who incident to pass and what to do in the first lesson.
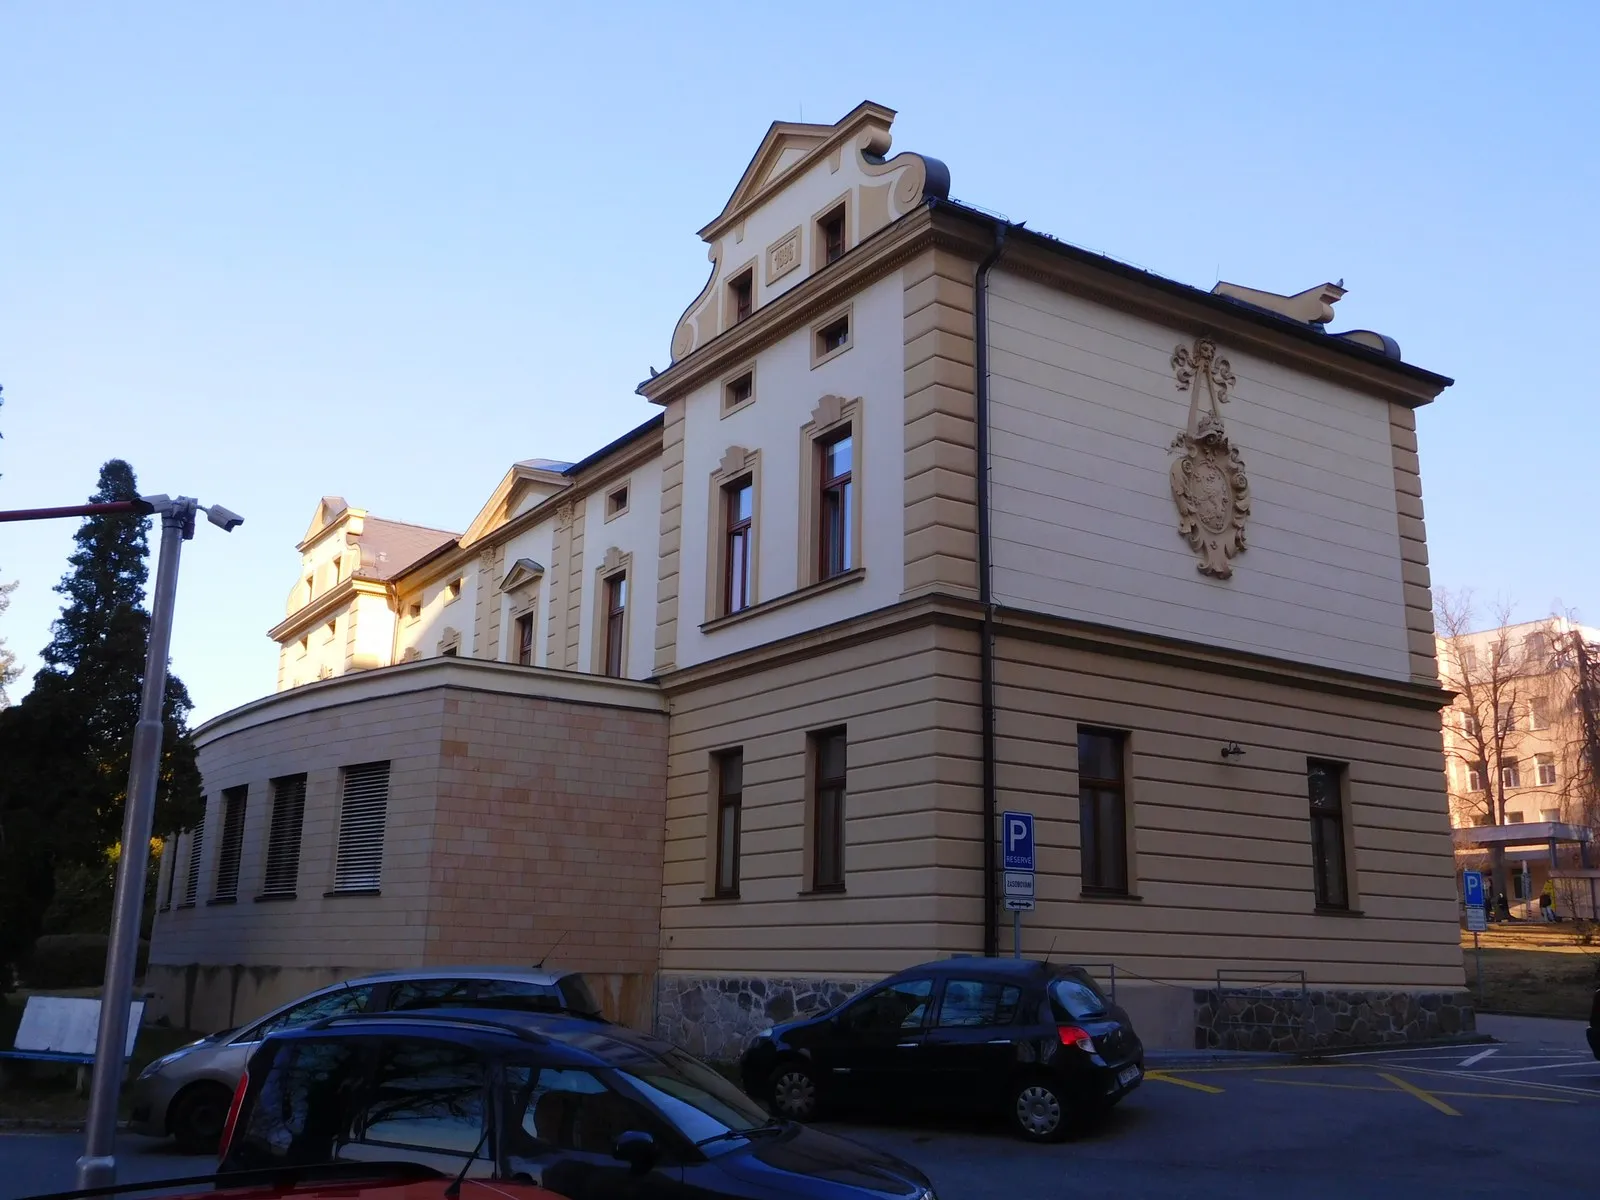
December 2019 Ryuk ransomware
On December 11, 2019, ransomware crippled hospital systems. Full operation did not resume until December 30, the damage exceeded 59 million crowns.
What we do with it: It started with email and poorly protected accounts. Cyber audit examines exactly these entry points.
Source: Czech Television (ČT24)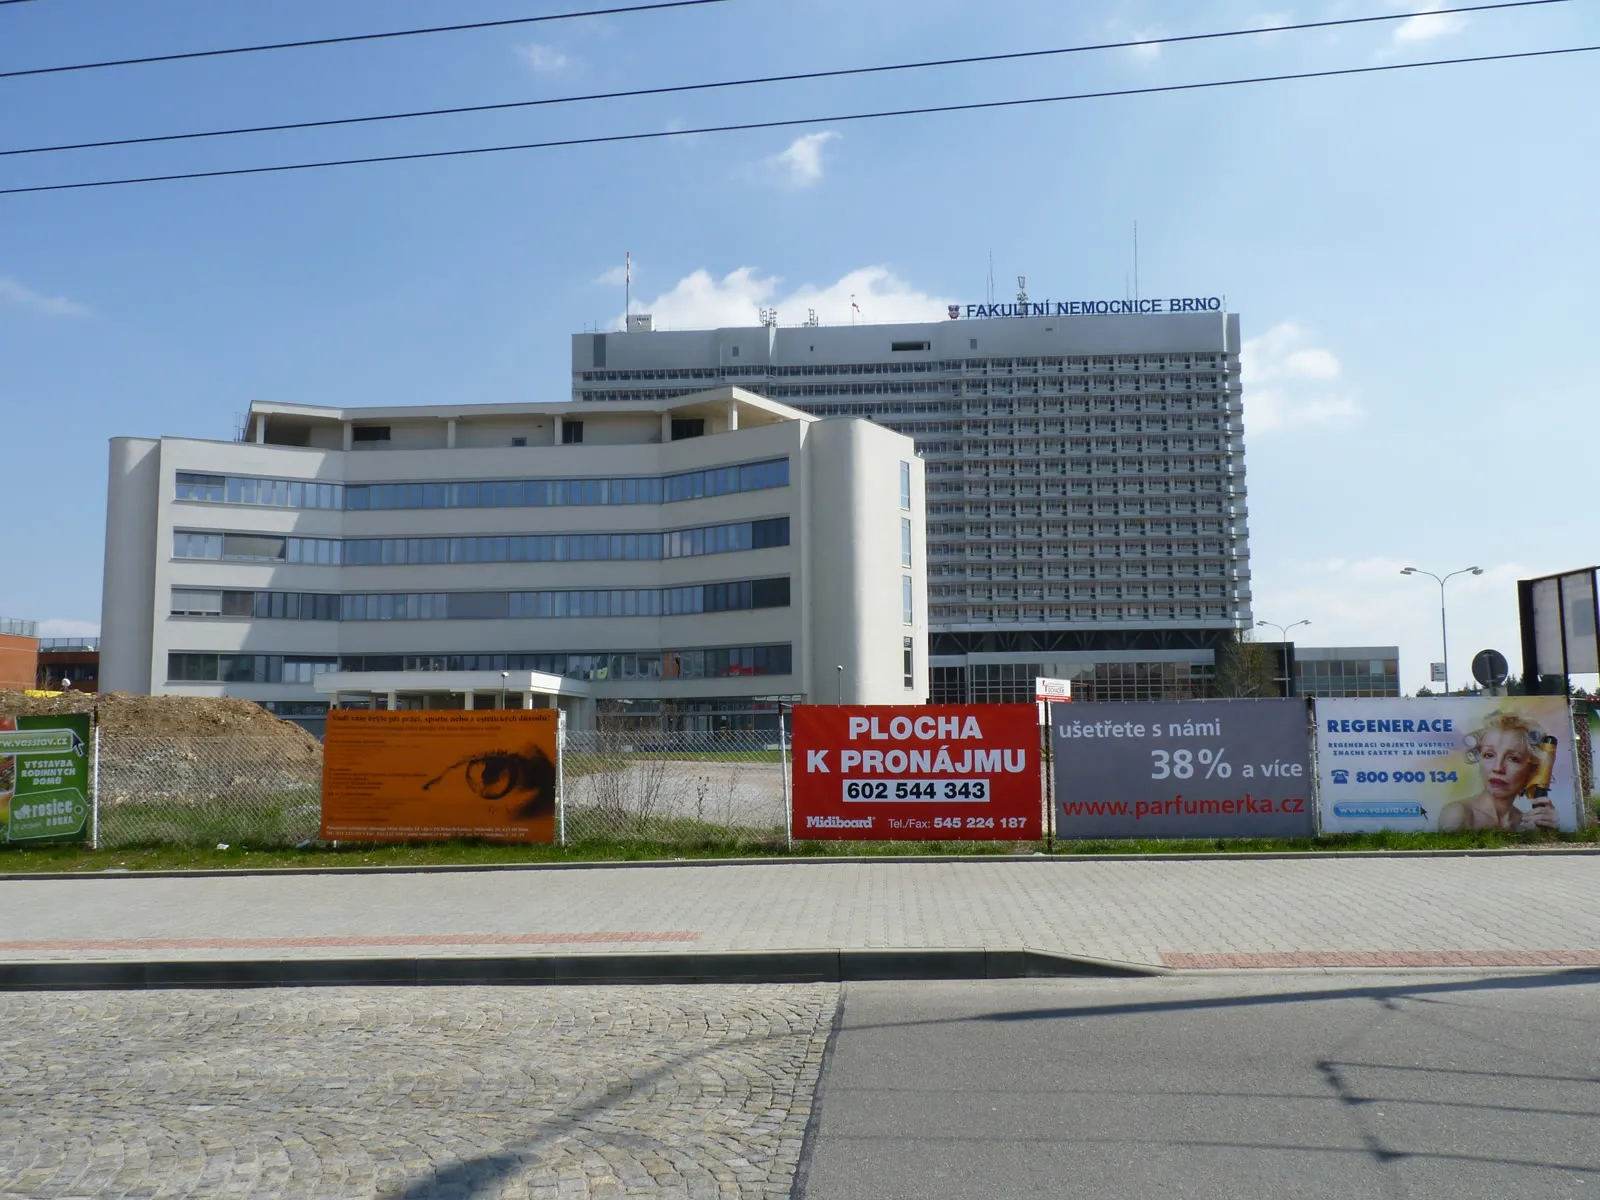

March 2020 · ransomware, the day after the state of emergency was declared
On March 13, 2020, a day after the state of emergency was declared, an attack encrypted the systems of the country's second largest hospital. Postponed operations, provisional damage of 150 million crowns.
What we do with it: One open attachment stopped the operation. That is why in the course we practice how to recognize phishing and what to do in the first lesson.
Source: Aktuálně.cz268
of cybersecurity incidents was recorded by NÚKIB in 2024, the most so far. Most often it was the public sector.
Source: NÚKIB, Report on the state of cyber security of the Czech Republic (2024)NIS2 and the new Cyber Security Act shift responsibility to management. An audit and a prepared team will cost less than a fine, downtime or data loss.
up to €10 million
or 2% of turnover: fines according to NIS2
Management is responsible
personal responsibility for the measures taken
24 / 72 h
statutory deadlines for reporting an incident
Suppliers
you are also responsible for the supply chain
Phishing, traffic analysis and risks in mobile. This is what a day with the team looks like.
It is practical. Management, operations and IT get a common language: what is the risk, who has what role and what to do in the first minutes of an incident.
Yes. You can take the course independently, but it will bring the most after auditing accounts, data, cameras and suppliers. The audit will find weak points, the course will teach the team to react.
Yes. Schools work with student data, staff accounts, cameras and vendors and must handle crisis communications. The course will translate cyber risks into normal school operations.
Cyber course
Describe the organization, the number of people and what you are dealing with. We will recommend the scope of the course.
Write whether it is a school, company or institution, how many participants there will be and what worries you the most. We will design the course.