






























01
Accounts and permissions
We will find out who has access to data, cameras and administration.
Cyber Security · Audit
Do you know who has access to your data? We will check accounts, deposits, cameras, suppliers and the team's first response.
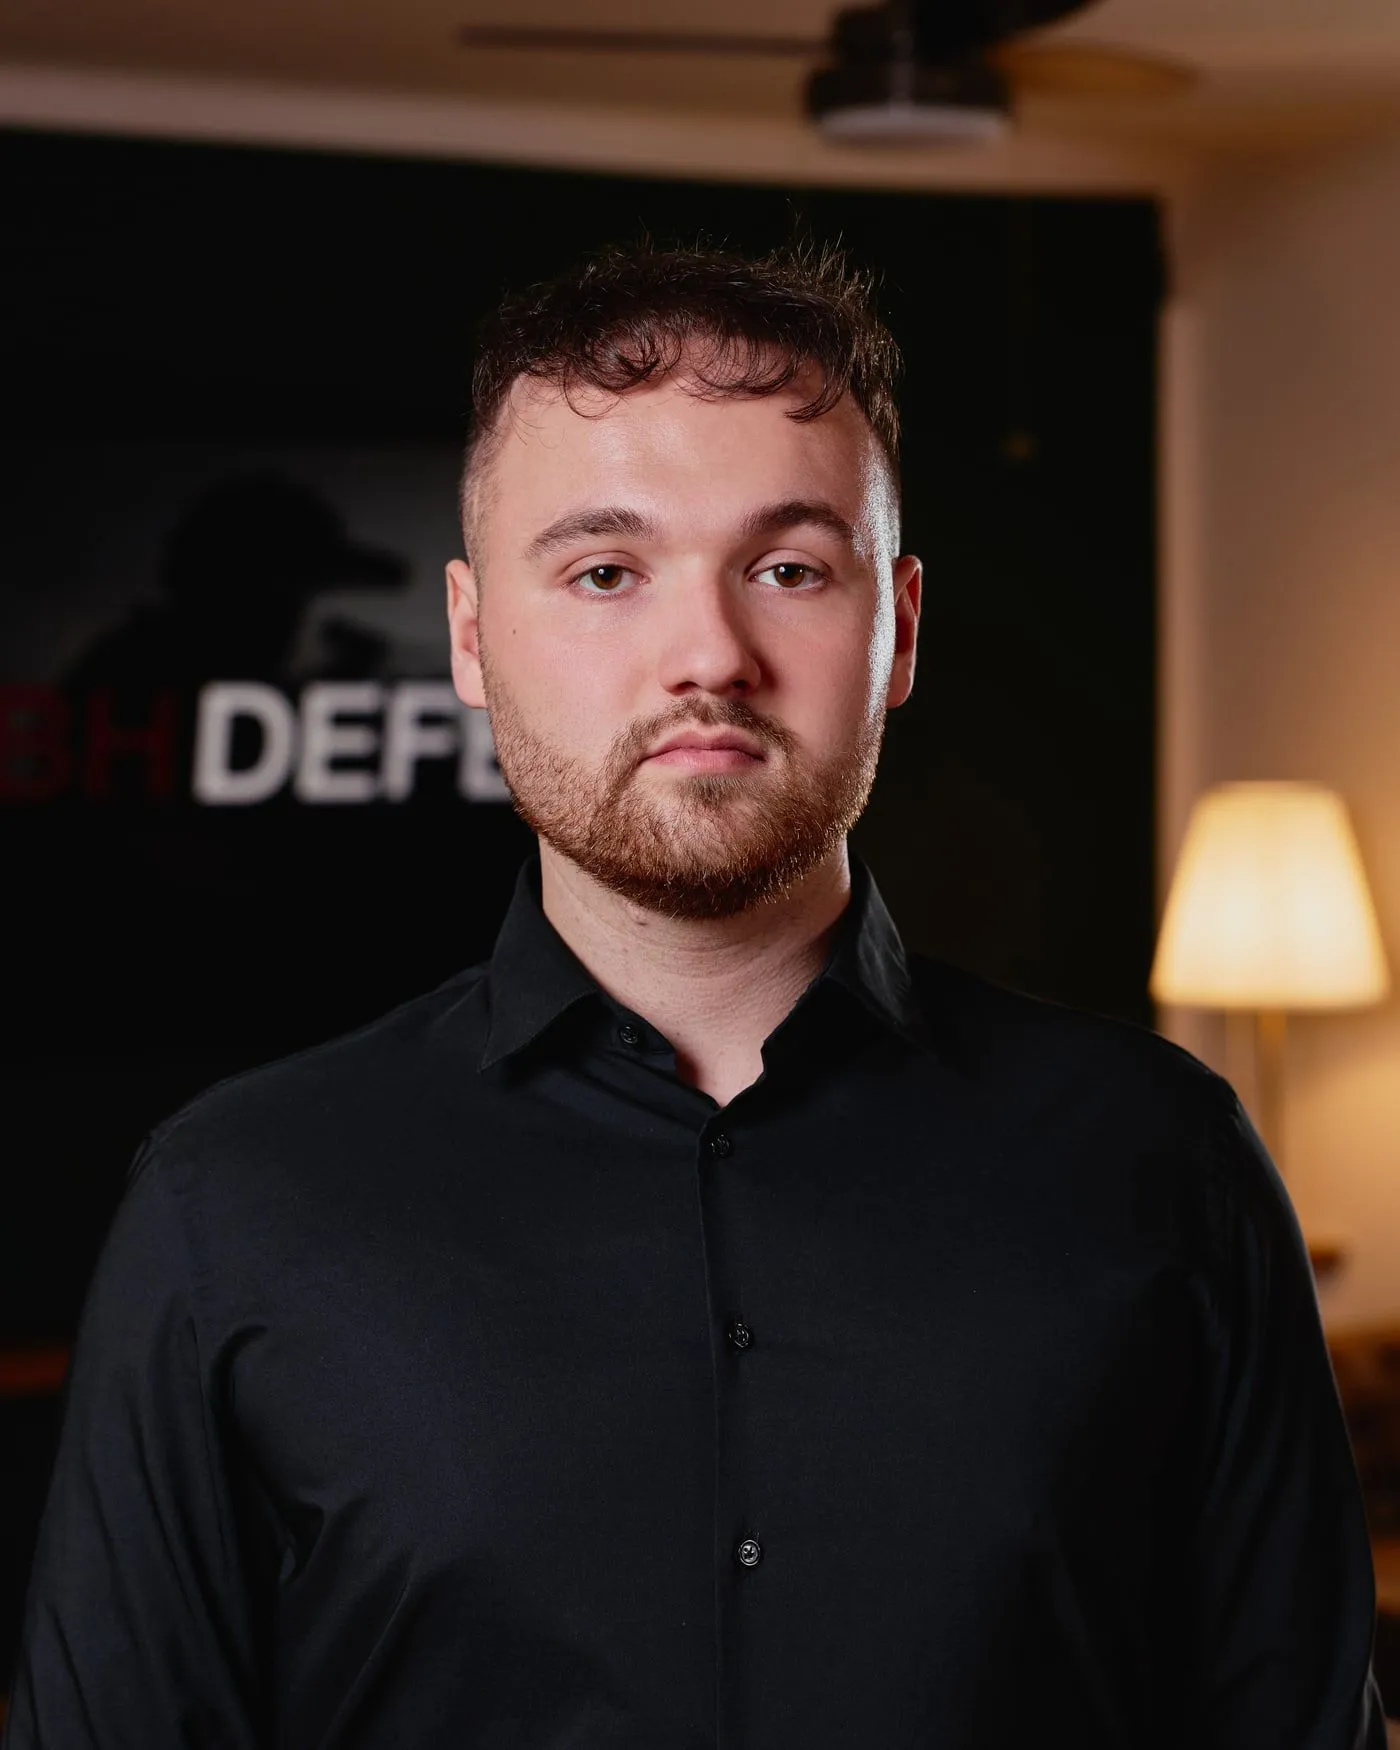
Division Director GBH Cyber
Your cybersecurity is not driven by a marketer, but by an engineer.
As a senior software engineer, he worked at IBM and at Trezor (SatoshiLabs), where he participated in the development of the Trezor Suite. At GBH, he connects cyber security with the group's physical infrastructure.
NÚKIB
responsibilities clearly
NIS2
impact on leadership
Data
accounts, roles, backups
Building
cameras and approaches
Practical impact
The result is decisions that will reduce risk in traffic.
Cyber audit it does not end with a long technical report. We will check accounts, dates, cameras and suppliers, and we will sort the findings into priorities that management understands.
Accounts, permissions, camera management and external IT management must be clear about who is responsible for what.
An audit separates critical data, backups, network and operational dependencies from things that can wait.
We will translate the technical findings into priorities, budget, responsible persons and further training of the team.

We will check accounts, data, suppliers, cameras and the physical mode of the building. Management gets sorted priorities.
Accounts and rights
Sensitive data
Suppliers
Building
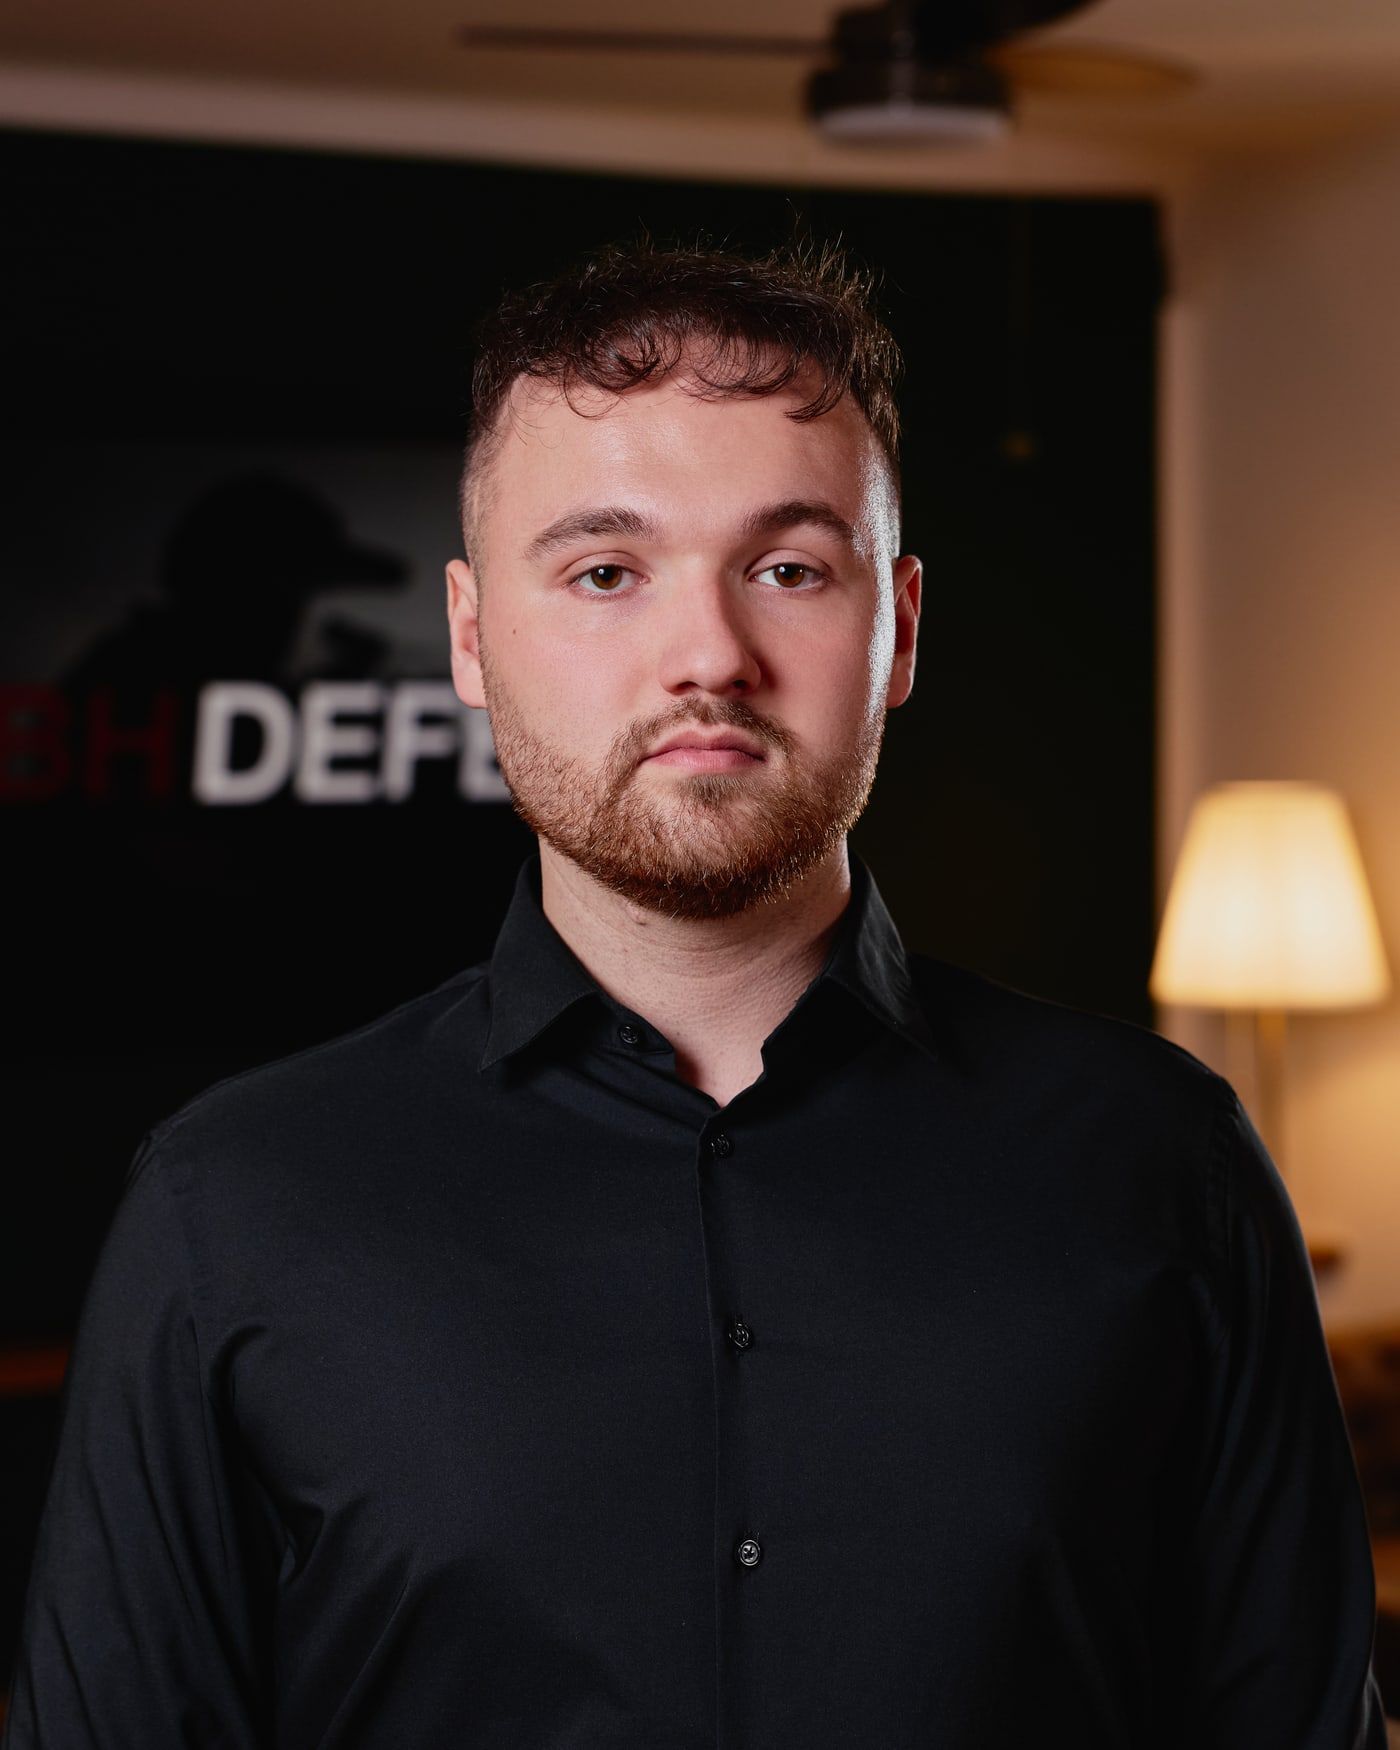
Division Director GBH Cyber
Adam Schinzel
Senior software engineer, IBM and Trezor/SatoshiLabs.
An audit is for management who need to know where the real risk is and what to change first.
01
We will find out who has access to data, cameras and administration.
02
We will verify that critical data can be recovered.
03
We will assess the camera system, inputs and building mode together.
04
We will verify where the responsibility of the external administrator ends.
05
Who calls, what is disconnected, what is recorded and who decides.
06
We will translate duties into steps for leadership.
Briefly and according to priorities: what to solve now, what to plan and what to transfer to training.
NIS2 and the new Act on cyber security they transfer responsibility to management. An audit and a prepared team will cost less than a fine, downtime or data loss.
up to €10 million
or 2% of turnover: fines according to NIS2
Management is responsible
personal responsibility for the measures taken
24 / 72 h
statutory deadlines for reporting an incident
Suppliers
you are also responsible for the supply chain
These are publicly documented incidents from the Czech Republic. Cyber audit examines the same entry points that this type of attack exploits: weak accounts, missing deposits, uncontrolled suppliers and the lack of a crisis procedure. We do not guarantee that you will never experience an incident. But we'll show you where you're vulnerable before an attacker finds out.
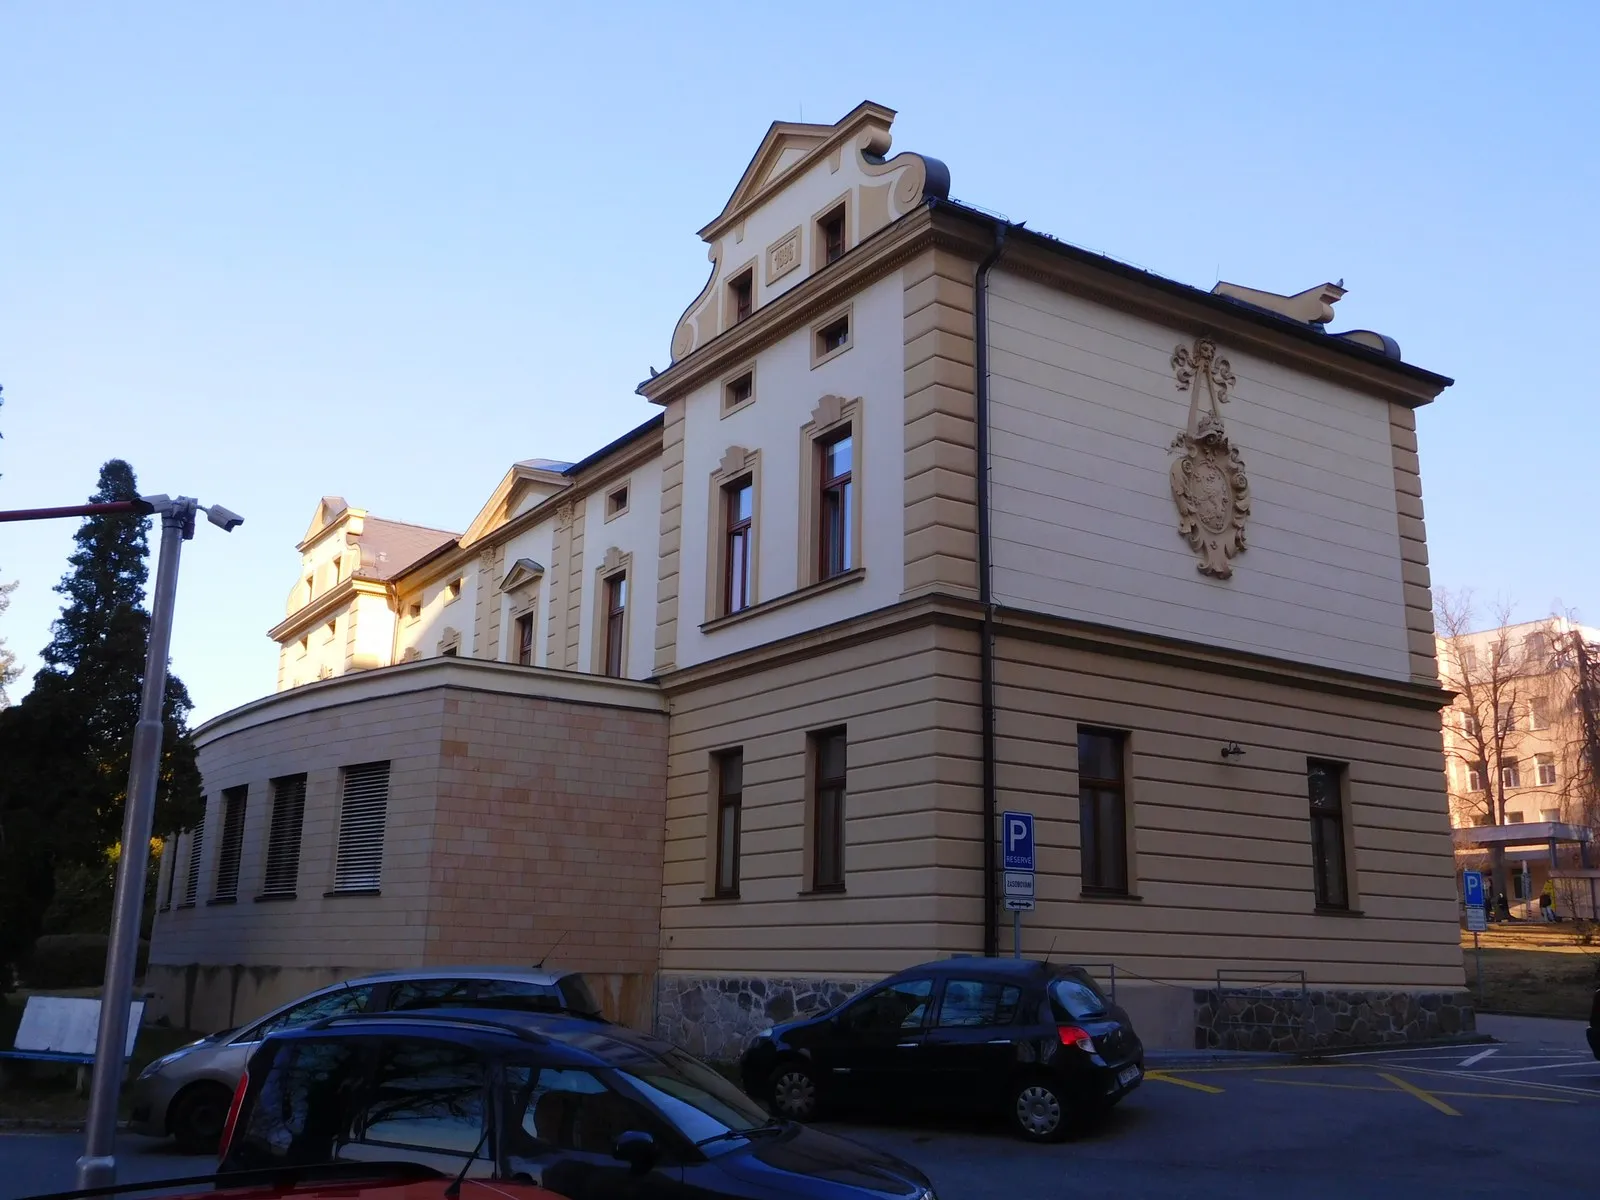
December 2019 Ryuk ransomware
On December 11, 2019, ransomware crippled hospital systems. Full operation did not resume until December 30, the damage exceeded 59 million crowns.
What we do with it: It started with email and poorly protected accounts. Cyber audit examines exactly these entry points.
Source: Czech Television (ČT24)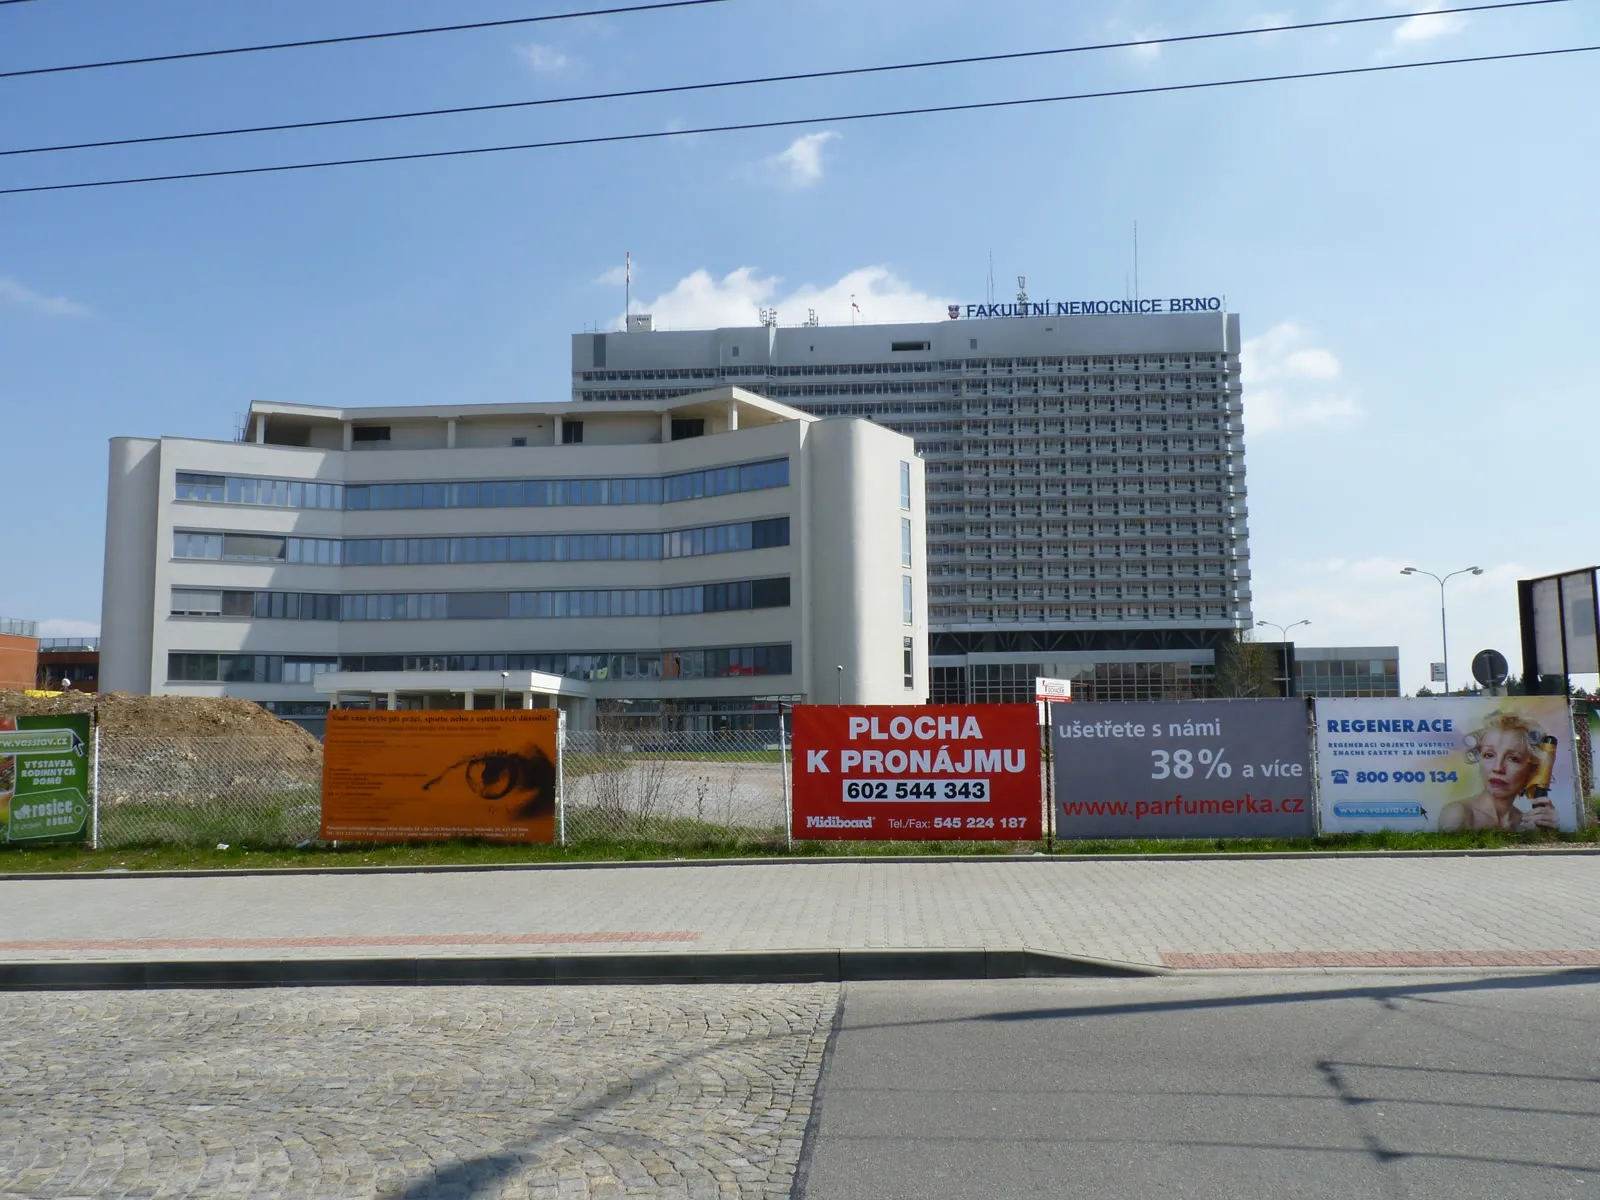

March 2020 · ransomware, the day after the state of emergency was declared
On March 13, 2020, a day after the state of emergency was declared, an attack encrypted the systems of the country's second largest hospital. Postponed operations, provisional damage of 150 million crowns.
What we do with it: One open attachment stopped the operation. That is why in the course we practice how to recognize phishing and what to do in the first lesson.
Source: Aktuálně.cz268
of cybersecurity incidents was recorded by NÚKIB in 2024, the most so far. Most often it was the public sector.
Source: NÚKIB, Report on the state of cyber security of the Czech Republic (2024)Operations center, traffic analysis, response to incident and physical approaches.
Nope. In schools, companies and institutions, data, cameras, approaches, suppliers and building mode are all connected. We therefore examine cyber security as part of the crisis preparedness of the entire organization.
Nope. The audit is also suitable for organizations where IT is provided by an external administrator. It is there that it is often unclear who manages the accounts and deposits, who is responsible for what and what the crisis procedure is.
Brief report with risks, priorities and recommended measures and procedure in the event of an incident. For a larger scale, we will supplement the team's follow-up training plan.
Cyber audit
Write us the type of organization, the number of locations and who manages your IT. We will propose a reasonable scope of the audit.
Write whether it is a school, company or institution, how many locations you have and how IT management is ensured. We will recommend the scope of the audit.